Checkpoint Smartdashboard Connection
Identity Awareness AD Query. Table of Contents Abstract. How AD Query ADQ works. Step 1 Communication with the Domain Controllers. Step 2 3 Extraction of the usermachine to IP Association and filtering undesirable association. Step 4 Applying the new Association with the user machine to the IP database. Various applicable scenarios. More about AD Query ADQ communication. I am trying to create a lab enviroment for CheckPoint NGX R65 I have a PC, with checkpoint installed VPN1 UTM Then i install on a second pc the. Simplified SitetoSite Virtual Private Network VPN The IPSec VPN Software Blade simplifies the creation and management of complex VPNs. SmartDashboard enables. Stateful Filtering and Stateful Inspection. The definition of stateful filtering seems to vary greatly among various product vendors and has developed somewhat, as. Security Gateway Domain Controller communication. Smart. Dashboard Domain Controller communication. Using AD Query with Exchange Servers. AD Query ADQ Performance Considerations. CheckPoint_SM15.png?w=300' alt='Checkpoint Smartdashboard Connection' title='Checkpoint Smartdashboard Connection' />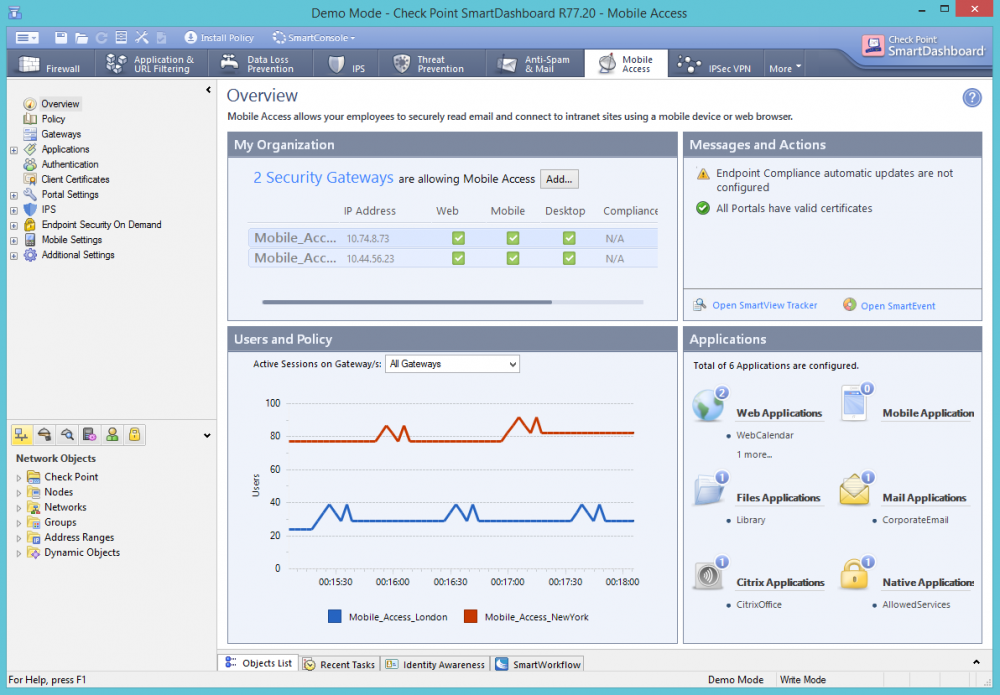


 Effect on the Security Gateway. Effect on the Domain Controllers. Bandwidth between the Security Gateway and the Domain Controllers. Configuring AD Query ADQ for more than one Security Gateway. AD Query ADQ Command Line interface. AD Query ADQ Advanced Configuration Options. Did you know that. You can configure AD Query ADQ to support non English names. You can configure each gateway to connect to different Domain Controllers in the same account unit. Identity Logging is now called AD Query. Related Solutions1 Abstract. AD Query ADQ is a clientless identity acquisition method. It is based on Active Directory integration and allows the Security Gateway to correlate Active Directory Users and machines to IP addresses in a method that is completely transparent to the user. When using AD Query ADQ, the Security Gateway connects to the Active Directory Domain Controllers using WMI, and subscribes to receive Security Event logs that are generated, by default, on the Domain Controllers, when users perform login. Using these event logs, the Security Gateway can correlate Active Directory Users and machines to IP addresses, and to enforce a user based policy. Note This article is not a substitute for the Identity Awareness Administration Guide, but rather a more detailed explanation of the feature and related technology. We strongly suggest reading the Identity Awareness Administration Guide R7. Deltav Advanced Unit Management Software on this page. R7. 5. 2. 0, R7. 5. R7. 5. 4. 0VS, R7. R7. 7 beforehand. How AD Query ADQ works. The steps in the AD Query example are listed below The Security Gateway registers to receive Security Event logs from the Active Directory Domain Controllers. A user logs in to a desktop computer using his Active Directory credentials. The user logs on to a Domain Controller DC. This DC and only it will have the logon security log those logs do not replicate to other DCs. The firewall queries all the DCs security logs and gets the logon security log. The Active Directory DC sends the Security Event log to the Security Gateway. The Security Gateway extracts the user and IP address information user namedomain, machine name and source IP address. The user initiates a connection to the Internet. The Security Gateway confirms that the user has been identified and allows him to access the Internet, based on the policy. AD Query ADQ employs the following four main steps Communication with the Domain Controllers and subscription for the relevant Security Event logs. Extracting the user andor machine to IP Association from the Event Log. Filtering undesirable associations. Applying the new Association with the user machine to the IP database. Steps Step 1 Communication with the Domain Controllers. After being configured, AD Query ADQ begins communication with all of the Domain Controllers in the configured account unit. The communication is a WMI query over DCE RPC, registering to receive all relevant Security Event logs from the Domain Controller. For Windows 2. 00. Domain Controllers, events 6. Windows 2. 00. 8 Domain Controllers events 4. From then on, any new relevant Security Event log will be sent to the Security Gateway, seconds from its creation time. AD Query ADQ does pull the Security Event log from the Active Directory every second 1 second or the Active Directory pushes the latest 1. Security Gateway that runs AD Query ADQ. The registration mechanism allows AD Query ADQ to receive new Security Event logs in a timely manner up to several seconds from generation time. It does not generate a lot of burden on the Domain Controller, as it already has the message in its memory, when it is sent to AD Query ADQ. Real life deployments on running AD environments, measured up to a 3 increase in CPU usage on the Domain Controllers, with an average of much less than 1. Most of the problems with AD Query ADQ happen in the communication phase since WMI runs over DCE RPC, which is a complicated and non firewall friendly protocol it starts on port 1. The first thing that you want to check when AD Query ADQ is not working is if something, on the local Security Gateway, or on the way to the Domain Controller is blocking this traffic. Refer to sk. 58. 88. AD Query traffic dropped by Check Point Security Gateway, for further details about how to diagnose and handle such problems. Step 2 3 Extraction of the usermachine to IP Association and filtering undesirable association. After AD Query ADQ successfully receives a Security Log event, it generates an Association between a user andor machine to an IP address. Afterwards, it may be filtered by both Implied and Configured filters. Implied filters. Implied filters will filter the following Associations Associations with an IP address of 1. AD Query ADQ will not be able to detect users working on the Domain Controller itself. Associations with general user name, such as NT AuthoritySystem. Associations with an IP address of one of the Check Point Security Gateways. The reason for this filtering is that Check Point Security Gateways may act as NAT Devices, hiding several IP addresses behind them. Step 4 Applying the new Association with the user machine to the IP database. Note The AD Query ADQ database is stored in the Kernel Tables. It does not survive reboot cpstop. Before discussing the process that happens each time a new association arrives and is applied to the database, we should note that the database is a mapping between IP address and a list of user and machine names, each of them with its own expiry time. For the sake of simplicity, well assume that the association includes either user or machine. If this is not the case, the association is handled as two subsequent associations, one including only the machine and the other one including the user. Various applicable scenarios. Various applicable scenarios New Association In case this IP address was unknown before this association, the association is added to the database with an expiry time of now the configured timeout by default, the configured timeout is 1. Existing Association If this Association for this IP address was known before, the expiry time is updated to now configured timeout The configured timeout is 1. Machine change If the machine has changed, all of the currently known user associations are revoked, as well as the current associated machine, and the new machine is added to the database with an expiry time of now configured timeout. New User If an unknown user association is encountered, and assume one user per IP is off default, the new association is added with an expiry time of now configured timeout The configured timeout is 1. User Change If an unknown user association is encountered, and assume one user per IP is on, all of the currently associated users are revoked, and the new association is added as the only user for this IP address.